Forum Is getting hacked [Big Thread]

Romxnus753AC

Romxnus753AC

Temp. Banned
Joined
Nov 25, 2024
Posts
5,087
Reputation
4,273
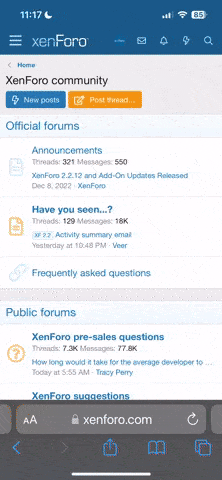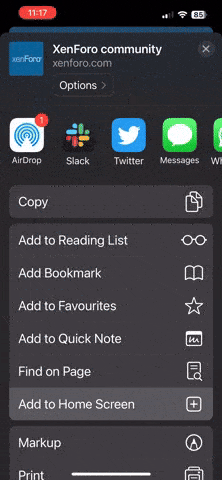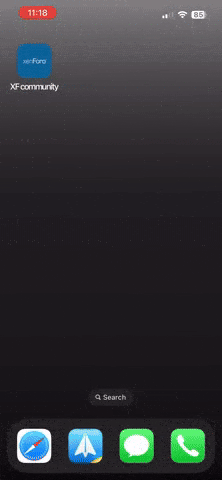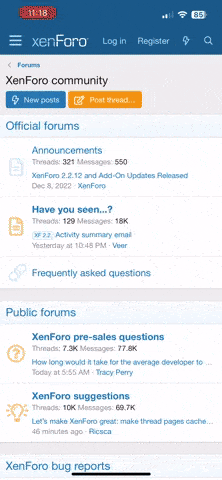
Screenshot 2026 09 30 02 03 37 424 comandroidchrome


@Master


I've been digging into the recent incidents and some of you need to hear this, because I don't think people realize how exposed we are right now.

First: this isn't just about stolen passwords.

Yes, the stealer logs are real. Yes, accounts are getting taken over. But there's a second problem nobody's talking about: the forum software itself has known vulnerabilities that were only patched in September 2026.

We're running XenForo. If the backend hasn't been updated to 2.3.13, we're sitting on at least a dozen documented CVEs. Here are the ones that matter:

OAuth2 authorization code reuse (CVE-2026-73311) — XenForo before 2.3.13 fails to invalidate authorization codes after use. An attacker who intercepts a code can replay it multiple times to generate token pairs for someone else's account. This bypasses the single-use guarantee that OAuth2 is supposed to provide.

OAuth2 refresh token replay (CVE-2026-73312) — Related issue. Refresh tokens aren't marked as consumed when the parent access token expires. An attacker can repeatedly submit the same refresh token to generate unlimited new token pairs, maintaining persistent access to the victim's account for the token's full lifetime.

Passkey MFA bypass (CVE-2026-73313) — This one is brutal. The passkey TFA provider performs a global credential lookup without verifying that the matched credential actually belongs to the user logging in. An attacker who knows a target's password can complete the target's two-step login using their own passkey. Affects both public forum login and ACP admin login. Reproduced on 2.3.12 (build 2031270).

Stored XSS via BB code (CVE-2026-35054) — XenForo before 2.3.9. Malicious scripts injected through BB code rendering get stored and executed when other users view the content. CVSS 6.4. This is how you get session hijacking en masse.

Missing authorization in force-agreement controller (CVE-2026-73318) — XenForo before 2.3.13. Any ACP administrator, regardless of assigned permissions, can access and submit force-agreement forms, forcing all users to re-agree to privacy policy or ToS. Low severity individually, but it shows the authorization model is broken in places.

There are more. Path traversal in the style archive importer on Windows deployments. SSRF in 2.3.8. Unfurl endpoint information disclosure. BBCode parser recursion. The full patch list for 2.3.13 covers 14 vulnerabilities reported by VulnCheck.

Why this matters right now

If the forum hasn't been updated past 2.3.12, every one of these is a potential entry point. Combined with the stealer logs, you have a situation where:

Accounts are being compromised via stolen credentials

The software has documented auth bypass and token replay flaws that make sessions harder to revoke

MFA — the thing we're all told to enable — can be bypassed if the backend isn't patched

What you should do

Enable 2FA anyway. It's still better than nothing, and it stops the low-effort attacks.

Don't reuse passwords. If your email is in a stealer log, your forum account is next.

If you're staff or have ACP access: verify the backend is on 2.3.13 or later. There's no reason to be on an older build.

If you're a regular user: you can't patch the server, but you can reduce your exposure. Check haveibeenpwned.com. Change your password if it's ever been used elsewhere.

The bottom line

We're not just dealing with compromised accounts. We're dealing with a forum running software that has known, documented, remotely exploitable authentication flaws. If nothing gets patched, the next wave won't need stolen passwords. It'll just walk through the front door.

I'm not trying to fearmonger. I'm saying: check the version. Patch the server. Enable 2FA. Do it now.

(@Master i can help y fix all of this, just delete my old cringe posts and ill do it for free, i dont wanna force my way into doing this without auth cuz yk its illigal)
 
Last edited:
  • +1
  • JFL
Reactions: lol, milkshake_addict, alurmo and 16 others
Nigga I’m not reading allat
 
  • +1
Reactions: Blondepawg'sDildo, Geoff2024, sugarfucker and 5 others
lol all our info has been seen by the feds already
 
  • +1
  • JFL
Reactions: bIiss, Geoff2024, thekey and 3 others
lol all our info has been seen by the feds already
Are y stupid, the site back end is exposed some can sql inject and destroy everything here
 
  • +1
Reactions: scuderia and IOD
Bumppppp
 
  • +1
Reactions: scuderia and IOD
I can only read english
 
  • +1
Reactions: scuderia, Jordan Barrett, IOD and 1 other person
wow, ill enable it!!:ogre::soy::feelsyay:
 
  • +1
Reactions: Jordan Barrett, IOD and Romxnus753AC
Is this like Osint Demon
 
  • JFL
  • +1
Reactions: IOD and erome
Is this like Osint Demon
The threat possibily, master didnt check the site for back ends and injections spots and there Is a alr a malware in here
 
  • +1
Reactions: IOD and Araneae
Path traversal in the style archive importer on Windows deployments. SSRF in 2.3.8. Unfurl endpoint information disclosure. BBCode parser recursion. The full patch list for 2.3.13 covers 14 vulnerabilities reported by VulnCheck.
how the parser of bbcode make user identity vulnerable?

and how the fuck you found those vulnerability

I spent days finding vulnerabilities just for formatting, and you managed to find some that can hack the forum? :feelspepo:


AYO wtf 😭
 
  • +1
Reactions: Jordan Barrett, IOD and Romxnus753AC
how the parser of bbcode make user identity vulnerable?

and how the fuck you found those vulnerability

I spent days finding vulnerabilities just for formatting, and you managed to find some that can hack the forum? :feelspepo:


AYO wtf 😭
I did cyber Security and we had a similar problem where a site had open injections cause of old software versions its similar to this one since the site was a premade forum like this one
 
  • +1
Reactions: IOD and shedontluv-U
how the parser of bbcode make user identity vulnerable?

and how the fuck you found those vulnerability

I spent days finding vulnerabilities just for formatting, and you managed to find some that can hack the forum? :feelspepo:


AYO wtf 😭
Anyway a BBCode can make ur identity vulnerable because of improper attribute sanitization (leading to Cross-Site Scripting) and direct resource loading (causing data leaks or Server-Side Request Forgery).
 
  • +1
  • Woah
Reactions: shedontluv-U and IOD
Stored XSS via BB code (CVE-2026-35054) — XenForo before 2.3.9. Malicious scripts injected through BB code rendering get stored and executed when other users view the content. CVSS 6.4. This is how you get session hijacking en masse.
this one litteraly don't fucking works, I tried

Just surviving the regex is impossible
The forum silently kills any HTML/script that ends up in the renderer.

It's literally written in the s9e repository
 
  • +1
Reactions: Jordan Barrett, Romxnus753AC and IOD
I did cyber Security and we had a similar problem where a site had open injections cause of old software versions its similar to this one since the site was a premade forum like this one
I spent fucking WEEKS finding way or tricks to bypass org formating limitations just for one thread :lasereyes:

And you you find as that much?
 
  • Woah
  • +1
Reactions: Jordan Barrett and Romxnus753AC
I appreciate that you took the time out of the day to protect me from hackers so Ill enable 2fa for you
 
  • +1
Reactions: Romxnus753AC
this one litteraly don't fucking works, I tried

Just surviving the regex is impossible
The forum silently kills any HTML/script that ends up in the renderer.

It's literally written in the s9e repository
Yeahs9e is solid. It's regex-based but hardened over years. You're not getting a script tag through a post, signature, or profile field. That door is basically welded shut


PS The real hole is still stolen passwords and session hijacking, not code injection through the formatter. Focus on 2FA, not on outsmarting the regex
 
  • +1
Reactions: shedontluv-U
I spent fucking WEEKS finding way or tricks to bypass org formating limitations just for one thread :lasereyes:

And you you find as that much?
What did u use to try doing this
 
  • +1
Reactions: shedontluv-U
I am who is behind all of this.
User data will be reached to the public if these demands are not met
1:
Master to cosplay in a furry suit and puur
Like a cat
Demand number two
: Listen to demand number one
 
  • +1
Reactions: Romxnus753AC
I am who is behind all of this.
User data will be reached to the public if these demands are not met
1:
Master to cosplay in a furry suit and puur
Like a cat
Demand number two
: Listen to demand number one
U cheeky boy
 
  • JFL
Reactions: lenvoalt
High iq
 
  • Woah
  • +1
Reactions: shedontluv-U and Romxnus753AC
Stored XSS via BB code (CVE-2026-35054) — XenForo before 2.3.9. Malicious scripts injected through BB code rendering get stored and executed when other users view the content. CVSS 6.4. This is how you get session hijacking en masse.
xss injection don't fucking works bro jfl

trust me I kinda tried ( for formating)

I managed to find lots of tricks

like encoding the payload in %encoding

everything in the id

still FUCKING got shit

how the fuck a nigga can make his parameter survive when the fucking regex look like that

(?:s/\w+/|@?[-\w]+/)?(?:[%\w]+-
)*(?'id'[0-9a-f]+)(?![%\w])#

???? org regular expression are more hypergamous than foid
 
Yeahs9e is solid. It's regex-based but hardened over years. You're not getting a script tag through a post, signature, or profile field. That door is basically welded shut


PS The real hole is still stolen passwords and session hijacking, not code injection through the formatter. Focus on 2FA, not on outsmarting the regex
fym focus on 2fa????

my goal is not fucking hacking the forum

Do you have a social ?
 
  • JFL
Reactions: TGUN.
What did u use to try doing this
huh

I put the balise like that

( balise ) ( balise )

And I looked for ways to get things between the balise

% encoding worked

nested embed just a false positive

and I tried to ask chatgpt but he keep reporting me and spamming the Daybreaker shit saying it was XSS injection but genuinely it was for formating, like I swear.
 
  • Hmm...
Reactions: Romxnus753AC
xss injection don't fucking works bro jfl

trust me I kinda tried ( for formating)

I managed to find lots of tricks

like encoding the payload in %encoding

everything in the id

still FUCKING got shit

how the fuck a nigga can make his parameter survive when the fucking regex look like that

(?:s/\w+/|@?[-\w]+/)?(?:[%\w]+-
)*(?'id'[0-9a-f]+)(?![%\w])#

???? org regular expression are more hypergamous than foid
Bro you're attacking the wrong layer. That regex isn't the defense, it's just the tokenizer.

s9e/TextFormatter doesn't render HtmL. It parses bBCode into an AST, then rebuilds it as safe HTML through a DOM builder. Every text node goes through htmlspecialchars(), every attribute value gets quoted and escaped. So even if your payload somehow survives the regex the renderer will just turn script into script before it ever hits the page.

Also Regex is a lexer rule for a media token. It yields an AST node. The renderer serializes via DOM builder with context-aware escaping (htmlspecialchars for text, quoted attributes). No string concat. Encoding tricks die at output, not input. The regex is irrelevant to XSS
 
  • Hmm...
Reactions: shedontluv-U
View attachment 5707838

@Master


I've been digging into the recent incidents and some of you need to hear this, because I don't think people realize how exposed we are right now.

First: this isn't just about stolen passwords.

Yes, the stealer logs are real. Yes, accounts are getting taken over. But there's a second problem nobody's talking about: the forum software itself has known vulnerabilities that were only patched in September 2026.

We're running XenForo. If the backend hasn't been updated to 2.3.13, we're sitting on at least a dozen documented CVEs. Here are the ones that matter:

OAuth2 authorization code reuse (CVE-2026-73311) — XenForo before 2.3.13 fails to invalidate authorization codes after use. An attacker who intercepts a code can replay it multiple times to generate token pairs for someone else's account. This bypasses the single-use guarantee that OAuth2 is supposed to provide.

OAuth2 refresh token replay (CVE-2026-73312) — Related issue. Refresh tokens aren't marked as consumed when the parent access token expires. An attacker can repeatedly submit the same refresh token to generate unlimited new token pairs, maintaining persistent access to the victim's account for the token's full lifetime.

Passkey MFA bypass (CVE-2026-73313) — This one is brutal. The passkey TFA provider performs a global credential lookup without verifying that the matched credential actually belongs to the user logging in. An attacker who knows a target's password can complete the target's two-step login using their own passkey. Affects both public forum login and ACP admin login. Reproduced on 2.3.12 (build 2031270).

Stored XSS via BB code (CVE-2026-35054) — XenForo before 2.3.9. Malicious scripts injected through BB code rendering get stored and executed when other users view the content. CVSS 6.4. This is how you get session hijacking en masse.

Missing authorization in force-agreement controller (CVE-2026-73318) — XenForo before 2.3.13. Any ACP administrator, regardless of assigned permissions, can access and submit force-agreement forms, forcing all users to re-agree to privacy policy or ToS. Low severity individually, but it shows the authorization model is broken in places.

There are more. Path traversal in the style archive importer on Windows deployments. SSRF in 2.3.8. Unfurl endpoint information disclosure. BBCode parser recursion. The full patch list for 2.3.13 covers 14 vulnerabilities reported by VulnCheck.

Why this matters right now

If the forum hasn't been updated past 2.3.12, every one of these is a potential entry point. Combined with the stealer logs, you have a situation where:

Accounts are being compromised via stolen credentials

The software has documented auth bypass and token replay flaws that make sessions harder to revoke

MFA — the thing we're all told to enable — can be bypassed if the backend isn't patched

What you should do

Enable 2FA anyway. It's still better than nothing, and it stops the low-effort attacks.

Don't reuse passwords. If your email is in a stealer log, your forum account is next.

If you're staff or have ACP access: verify the backend is on 2.3.13 or later. There's no reason to be on an older build.

If you're a regular user: you can't patch the server, but you can reduce your exposure. Check haveibeenpwned.com. Change your password if it's ever been used elsewhere.

The bottom line

We're not just dealing with compromised accounts. We're dealing with a forum running software that has known, documented, remotely exploitable authentication flaws. If nothing gets patched, the next wave won't need stolen passwords. It'll just walk through the front door.

I'm not trying to fearmonger. I'm saying: check the version. Patch the server. Enable 2FA. Do it now.

(@Master i can help y fix all of this, just delete my old cringe posts and ill do it for free, i dont wanna force my way into doing this without auth cuz yk its illigal)
I don’t think master cares enough tbh. Good for you trying to help though
 
  • +1
Reactions: Romxnus753AC
fym focus on 2fa????

my goal is not fucking hacking the forum

Do you have a social ?
I use my own encrpytion software if we got to talk about limit of legal things i can say, i have a social but i dont want to share If u got one ill add u
 
  • +1
Reactions: shedontluv-U
not really
 
  • Hmm...
  • JFL
Reactions: shedontluv-U and Romxnus753AC
this shit makes my head spin
 
  • JFL
Reactions: TGUN.
huh

I put the balise like that

( balise ) ( balise )

And I looked for ways to get things between the balise

% encoding worked

nested embed just a false positive

and I tried to ask chatgpt but he keep reporting me and spamming the Daybreaker shit saying it was XSS injection but genuinely it was for formating, like I swear.
BBCode builds an AST and re-parents orphans when parent/child rules fail. Percent-encoding is URL tokenization, not a bypass. Nested embeds are auto-close artifacts, structural siblings not children. ChatGPT misfires on tag patterns, ignore it
 
  • JFL
Reactions: shedontluv-U
Cracking Up Lol GIF by STRAPPED!


"s9e don't render html"

half the media use a html in their fucking regex
LITTERALY Falstad use an html in his regex bhai

And guess what?

false what is the only media with all his parameter in the user payload


you telling yourself wow I could easily put my own html in the src ( for formating) or inject script

but no

running=false
and guess what 😹
 
  • +1
Reactions: threadeffort
BBCode builds an AST and re-parents orphans when parent/child rules fail. Percent-encoding is URL tokenization, not a bypass. Nested embeds are auto-close artifacts, structural siblings not children. ChatGPT misfires on tag patterns, ignore it
nested embed fuck works I can prove it

chatgpt fucking flagged my account

look into Prezi you will see
 
  • +1
Reactions: threadeffort
Cracking Up Lol GIF by STRAPPED!


"s9e don't render html"

half the media use a html in their fucking regex
But that HTML is the template. You control the UrL, not the markup.l

The regex pulls a string out of your URL, and that string gets injected into an attribute that's already quoted and escaped. You'd have to break the quoting to escape the template, and that's where the escaping layer stops you not the regex.
 
  • +1
Reactions: shedontluv-U
not a bypass
BRO

YES ITS A FUCKING BYPASS WHAT ARE YOU FUCKING TALKING ABOUT ?????

WHAT ARE YOU ON ???

YOU LITTERALY NEED THE URL BETWEEN THE BALISE ??

I WAS LITTERALY ABLE TO PUT MY BROWSER IN MY OWN THREAD NIGGA
 
  • +1
Reactions: threadeffort
nested embed fuck works I can prove it

chatgpt fucking flagged my account

look into Prezi you will see
Not saying you're wrong, but "nested embed fuck works" isn't a PoC. Prezi is a known XSS surface (WordPress plugin had stored XSS, CVE-2025-26538), so I believe the angle is plausible. What I don't believe yet is that it survives s9e + renderer + CSP on this site
 
  • +1
Reactions: shedontluv-U
But that HTML is the template. You control the UrL, not the markup.l

The regex pulls a string out of your URL, and that string gets injected into an attribute that's already quoted and escaped. You'd have to break the quoting to escape the template, and that's where the escaping layer stops you not the regex.
you can change the render from the user payload

just depends what media you using

but some are genuinely useless

for exemple

circuitjs.html?whiteBackground=true&running=false&cct

this one I don't remember if you encode it or no but just remove the screen

but some are really useful but most are not
 
BRO

YES ITS A FUCKING BYPASS WHAT ARE YOU FUCKING TALKING ABOUT ?????

WHAT ARE YOU ON ???

YOU LITTERALY NEED THE URL BETWEEN THE BALISE ??

I WAS LITTERALY ABLE TO PUT MY BROWSER IN MY OWN THREAD NIGGA
iframe in a post isn't XSS, same-origin walls it off from parent.document and XF.config.csrf. For it to be a real bypass the regex capture has to break out of src="..." quoting and land a javascript: URI or an onload handler on the iframe itself, meaning the template does unescaped interpolation. Otherwise it's just an embed every YouTube one does the same. Show parent.XF.config.csrf returning a value from inside the frame and it's real, otherwise it's nothing
 
  • Love it
Reactions: shedontluv-U
Not saying you're wrong, but "nested embed fuck works" isn't a PoC. Prezi is a known XSS surface (WordPress plugin had stored XSS, CVE-2025-26538), so I believe the angle is plausible. What I don't believe yet is that it survives s9e + renderer + CSP on this site
BRO I DON'T FUCKING WANT TO DO XSS INJECTION I JUST WANT FUCKING PRETTY COLOR AND AESTHETIC FORMATING :lasereyes:
 
you can change the render from the user payload

just depends what media you using

but some are genuinely useless

for exemple

circuitjs.html?whiteBackground=true&running=false&cct

this one I don't remember if you encode it or no but just remove the screen

but some are really useful but most are not
Give me time towrite Bro
 
  • JFL
Reactions: shedontluv-U

Similar threads

Mai Sakurajima.
Replies
4
Views
35
Mai Sakurajima.
Mai Sakurajima.
dhusc
Replies
7
Views
70
ToDelirium
ToDelirium
TGUN.
Replies
52
Views
328
sonic55555
S

Users who are viewing this thread

  • americanpakitruvcel
Back
Top