

Romxnus753AC
Temp. Banned
- Joined
- Nov 25, 2024
- Posts
- 5,087
- Reputation
- 4,273
- OP
- #51
BRO GIVE ME TIMEBRO I DON'T FUCKING WANT TO DO XSS INJECTION I JUST WANT FUCKING PRETTY COLOR AND AESTHETIC FORMATING
Follow along with the video below to see how to install our site as a web app on your home screen.
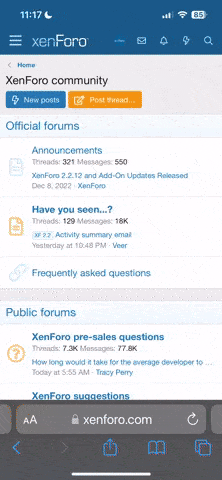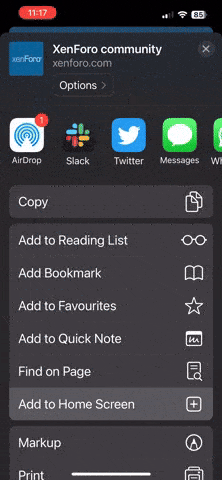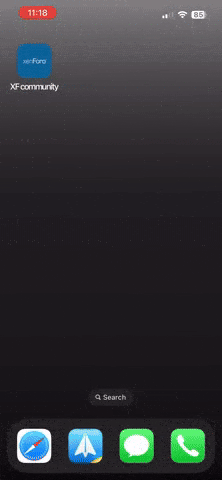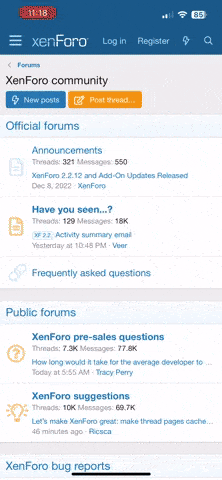
Note: this_feature_currently_requires_accessing_site_using_safari
BRO GIVE ME TIMEBRO I DON'T FUCKING WANT TO DO XSS INJECTION I JUST WANT FUCKING PRETTY COLOR AND AESTHETIC FORMATING


YES LITTERALYsrc="..."
Its illigal thoBRO I DON'T FUCKING WANT TO DO XSS INJECTION I JUST WANT FUCKING PRETTY COLOR AND AESTHETIC FORMATING
sorryGive me time towrite Bro

who decided that ?Its illigal tho
Opsec level:ton618I used a different email proton mail to sign up w opsec
Cuz the site isnt urswho decided that ?
CSP still stops it from firing, and the URL is logged everywhere. That's why the only clean move is a DM to staff but staff here does nothingYES LITTERALY
some media fetch the real website and other use an html and the URL in the whole payload
if you control the Url you can contrôle the payload
and maybe add a second src or remove the first one
I was able to do it I think but It exposes the person who does it

yea but I was trying to make a botb with thatCuz the site isnt urs
They always did but this is about if ur lm.org account gets to see another day (if someone does something)so what does this mean?
Feds can see my info
Feds can always see your info thomasso what does this mean?
Feds can see my info
so what does this mean?
Feds can see my info
keep it for yourself Any template-based media embed that lets you break attribute quoting is a real bug, DM it to staff with the exact tag and URL don't thread it. Credit without exposure.yea but I was trying to make a botb with that
and I was going to report all the vulnerability to admin ( not the formatting one )
So someone can just delete my account?They always did but this is about if ur lm.org account gets to see another day (if someone does something)
op breached the forum to delete some of his cringe threads JFL(@@Master i can help y fix all of this, just delete my old cringe posts and ill do it for free, i dont wanna force my way into doing this without auth cuz yk its illigal)
Thats if they hack master account which is exposed like all of our account BECAUSE @Master WONT UPDATE THE SOFTWARE THIS SITE WAS BUILT ONSo someone can just delete my account?
How am I going to be able to make interactive threads then?DM it to staff with the exact tag and URL don't thread it. Credit without exposure.
I Need money for my company not tsop breached the forum to delete some of his cringe threads JFL
jbv
Just buy Vip bro
org is still on PHP ? or sum shit like that ??Thats if they hack master account which is exposed like all of our account BECAUSE @Master WONT UPDATE THE SOFTWARE THIS SITE WAS BUILT ON
waterI Need money for my company not ts
How am I going to be able to make interactive threads then?
huh ???
Php is not the issue
So just locally or u want it server wisecan you help me tho
like find a way to make media interactive without exposing anyone?


U will lose Ur vip and mod if someone just executes a few hundred long py codeOh no
give me a fucking exemple how the fuckXenForo's the issue, not PHP.
MFA bypass in the passkey provider (CVE-2026-73313): global credential lookup, no check that the passkey belongs to the logging-in user. Know the password, sign the challenge with your own key, second factor done. Forum and ACP both.
OAuth2 code reuse (73311) and refresh token replay (73312): codes aren't invalidated after exchange, refresh tokens aren't consumed when the parent expires. Replay for days.
Stored XSS via BB code pre-2.3.9 (35054). SSRF in the PayPal webhook cert URL (73315).
All patched in 2.3.13, September 2026. If the backend isn't there yet, that's the whole attack surface. Tell @Master to push the update.
hack this forum and I come to your house
fuck you mean locally ( sorry for the bad words mister )So just locally or u want it server wise


wait you can do that ?U will lose Ur vip and mod if someone just executes a few hundred long py code


banned him for exposing a problem???Bros not even using a vpn
Nopebanned him for exposing a problem???

Banned him because you were gonna expose the problem first?Nope
not to mention the admin panel's directory isn't randomizedView attachment 5707838
@Master
I've been digging into the recent incidents and some of you need to hear this, because I don't think people realize how exposed we are right now.
First: this isn't just about stolen passwords.
Yes, the stealer logs are real. Yes, accounts are getting taken over. But there's a second problem nobody's talking about: the forum software itself has known vulnerabilities that were only patched in September 2026.
We're running XenForo. If the backend hasn't been updated to 2.3.13, we're sitting on at least a dozen documented CVEs. Here are the ones that matter:
OAuth2 authorization code reuse (CVE-2026-73311) — XenForo before 2.3.13 fails to invalidate authorization codes after use. An attacker who intercepts a code can replay it multiple times to generate token pairs for someone else's account. This bypasses the single-use guarantee that OAuth2 is supposed to provide.
OAuth2 refresh token replay (CVE-2026-73312) — Related issue. Refresh tokens aren't marked as consumed when the parent access token expires. An attacker can repeatedly submit the same refresh token to generate unlimited new token pairs, maintaining persistent access to the victim's account for the token's full lifetime.
Passkey MFA bypass (CVE-2026-73313) — This one is brutal. The passkey TFA provider performs a global credential lookup without verifying that the matched credential actually belongs to the user logging in. An attacker who knows a target's password can complete the target's two-step login using their own passkey. Affects both public forum login and ACP admin login. Reproduced on 2.3.12 (build 2031270).
Stored XSS via BB code (CVE-2026-35054) — XenForo before 2.3.9. Malicious scripts injected through BB code rendering get stored and executed when other users view the content. CVSS 6.4. This is how you get session hijacking en masse.
Missing authorization in force-agreement controller (CVE-2026-73318) — XenForo before 2.3.13. Any ACP administrator, regardless of assigned permissions, can access and submit force-agreement forms, forcing all users to re-agree to privacy policy or ToS. Low severity individually, but it shows the authorization model is broken in places.
There are more. Path traversal in the style archive importer on Windows deployments. SSRF in 2.3.8. Unfurl endpoint information disclosure. BBCode parser recursion. The full patch list for 2.3.13 covers 14 vulnerabilities reported by VulnCheck.
Why this matters right now
If the forum hasn't been updated past 2.3.12, every one of these is a potential entry point. Combined with the stealer logs, you have a situation where:
Accounts are being compromised via stolen credentials
The software has documented auth bypass and token replay flaws that make sessions harder to revoke
MFA — the thing we're all told to enable — can be bypassed if the backend isn't patched
What you should do
Enable 2FA anyway. It's still better than nothing, and it stops the low-effort attacks.
Don't reuse passwords. If your email is in a stealer log, your forum account is next.
If you're staff or have ACP access: verify the backend is on 2.3.13 or later. There's no reason to be on an older build.
If you're a regular user: you can't patch the server, but you can reduce your exposure. Check haveibeenpwned.com. Change your password if it's ever been used elsewhere.
The bottom line
We're not just dealing with compromised accounts. We're dealing with a forum running software that has known, documented, remotely exploitable authentication flaws. If nothing gets patched, the next wave won't need stolen passwords. It'll just walk through the front door.
I'm not trying to fearmonger. I'm saying: check the version. Patch the server. Enable 2FA. Do it now.
(@Master i can help y fix all of this, just delete my old cringe posts and ill do it for free, i dont wanna force my way into doing this without auth cuz yk its illigal)
he's just assuming the forum is not updated to the current version and going off an exploit directory, I would think a forum this large would have an auto update features so these exploits might be uselessI spent fucking WEEKS finding way or tricks to bypass org formating limitations just for one thread
And you you find as that much?


